Article
GitHub Actions Security Flaws: What Developers Need to Know Critical vulnerabilities in GitHub Actions have sparked serious concerns among developers and cybersecurity experts. These GitHub Actions security flaws—especially linked to the pull_request_target trigger—could allow attackers to take control of open source repositories or leak sensitive ...
Read article
GitHub Actions Security Flaws: What Developers Need to Know Critical vulnerabilities in GitHub Actions have sparked serious concerns among developers and cybersecurity experts. These GitHub Actions security flaws—especially linked to the pull_request_target trigger—could allow attackers to take control of open source repositories or leak sensitive credentials. Sysdig’s Threat Research Team recently demonstrated how a single misconfiguration in widely trusted repositories like MITRE and Splunk could let hackers gain dangerous access. If you're using GitHub for automation, knowing how these issues occur and how to fix them is vital for keeping your projects secure. Understanding the GitHub Actions security flaws GitHub Actions simplifies continuous integration and deployment but can also be a backdoor for malicious activity if not configured correctly. The core issue lies in how pull_request_target runs workflows in the context of the main branch—even for code submitted by external contributors. This opens the door to exploits where attackers can inject malicious code, steal GitHub secrets like tokens and passwords, or even hijack automated workflows. Despite documentation and best practice guides, many repositories—especially open source ones—still rely on risky setups that leave them vulnerable. High-profile examples raise the alarm Recent proof-of-concept attacks have shown how easily these vulnerabilities can be abused. Sysdig’s team demonstrated exploits on repositories from security giants like MITRE and Splunk, raising alarms across the developer community. These incidents highlight a disturbing truth: even organizations with strong cybersecurity standards can overlook GitHub Actions misconfigurations. This reinforces the need for teams to audit their workflows and eliminate high-risk triggers or overly permissive settings that expose their codebase to attacks. How developers can protect their GitHub workflows Preventing GitHub Actions security flaws starts with awareness and cautious configuration. Avoid using pull_request_target unless absolutely necessary. When you do use it, make sure workflows never check out external code or expose secrets. Developers should regularly review GitHub security advisories, enforce strict branch protections, and adopt least-privilege principles for tokens. Tools like Dependabot and secret scanning can help flag issues early, while third-party platforms like Sysdig can provide deeper insights into workflow behaviors and security.
 Practical Mobile Tools for Notes, Navigation and Location Exploration
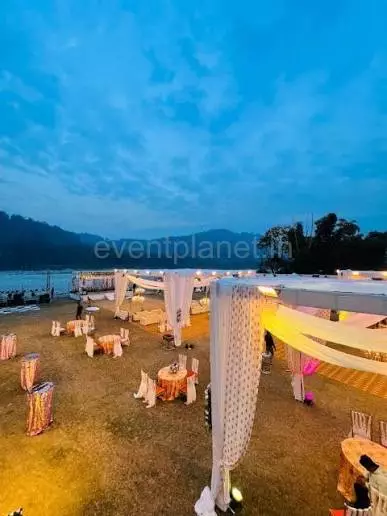 Destination Wedding in Uttarakhand: Celebrate Your Special Day Amid the Mountains
 Grocery App Development Company: Revolutionizing the Process of Grocery Purchase
 Microsoft’s Xbox Labs to Test Game Decompiling and Recompiling
 Launch Vibe-Coded Apps on the Google Play Store
 YouTube Premium Adds Background Listening While Driving